You can already build this yourself. That’s not in question — if you’re reading this, you’ve cleared the baseline where “can I hand-roll an agent” is even a real question. The problem is that the market keeps offering you two insulting options: shallow no-code toys that cap you beneath your own skill, or the chance to rebuild the entire substrate — hosting, orchestration, secrets, observability, upgrades — in raw code before you ever get to the part you actually care about.
That’s the false choice this article is here to dismantle. The real decision isn’t capability; it’s where you spend your scarce engineering hours. So we’ll run the three axes everyone asks about — security, cost, control — and add the fourth one the toys never mention, because it’s the one that determines whether your build is an asset or a trap: exit.
TL;DR: Self-host when data sovereignty, hard cost ceilings, or full-stack control are non-negotiable. Go managed when you want the security and ops substrate handled so you can spend your depth on cognition, not plumbing. Either way, design for exit from day one.
What is the real difference between self-hosted and managed AI agent platforms?
The difference isn’t “who runs your code” — it’s which layer of the stack is your problem. Self-hosted hands you the entire runtime; managed owns the substrate and exposes primitives. The rest is detail.
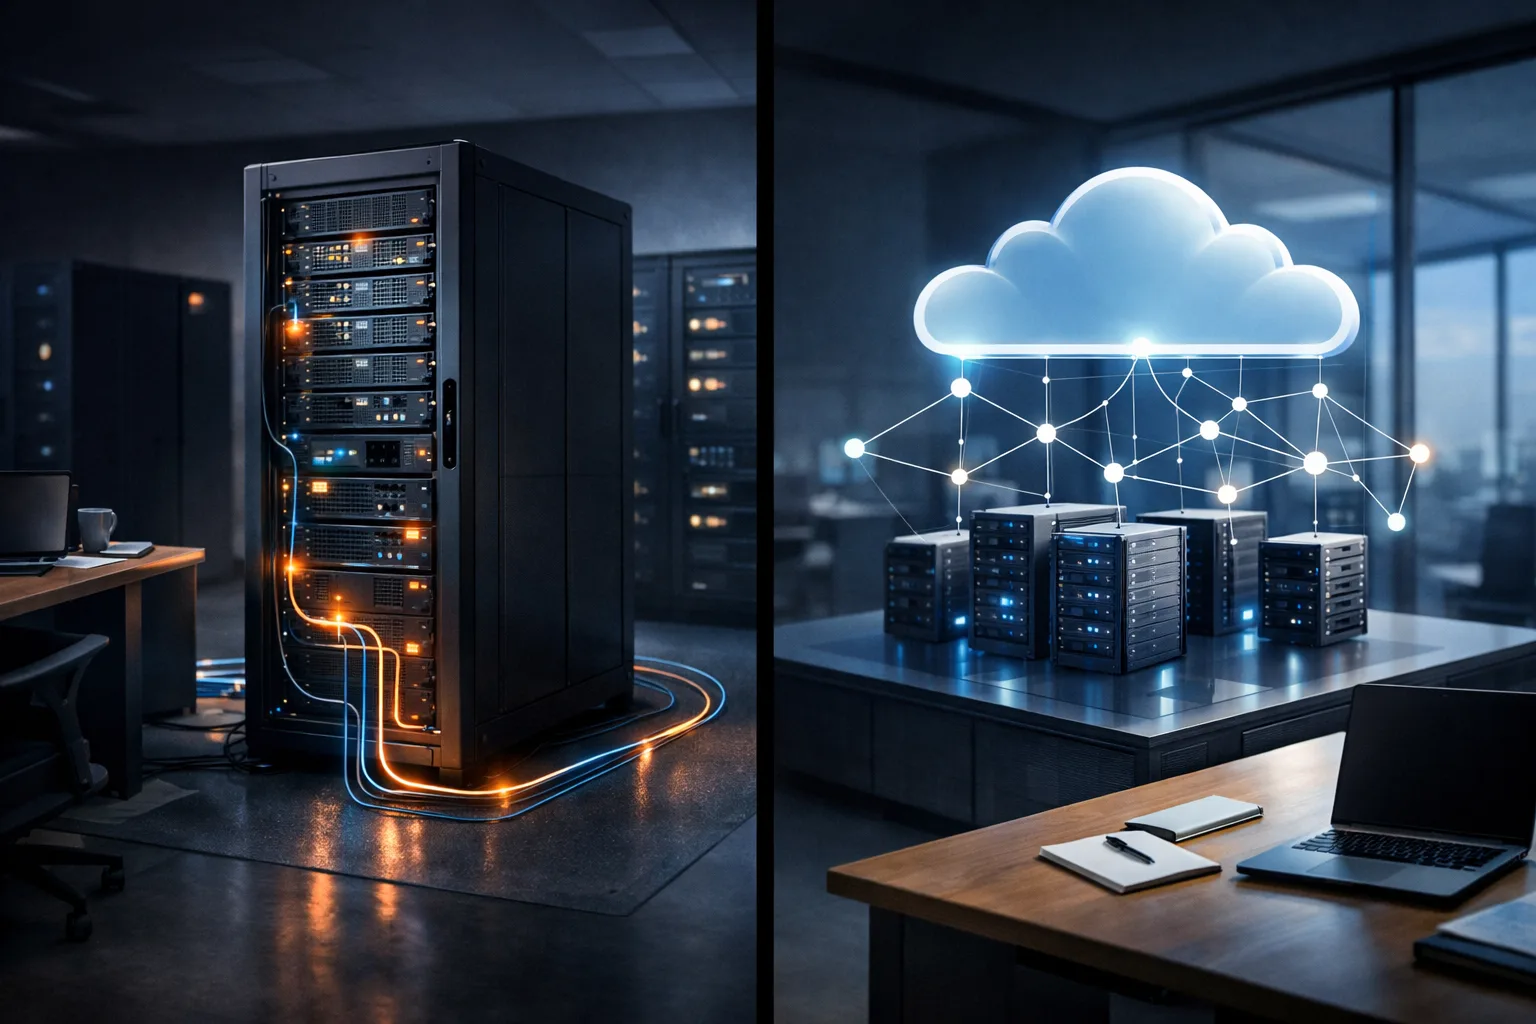
The useful mental model is a layer split, not a binary. Every AI agent system has a control plane — the orchestration, scheduling, memory, permissions, and state that decide what runs and when — and a data plane — the actual execution: model calls, tool invocations, the prompts and context flowing through.
Self-hosting means you own both planes, end to end. You run the orchestration, you manage the secrets, you patch the runtime, you stare at the GPU idle-time graphs at 2 a.m. Managed means the vendor owns the substrate — hosting, orchestration, upgrades, security controls — and exposes you the primitives on top.
The deeper distinction is single-tenant vs multi-tenant. “Self-hosted” almost always means single-tenant: your data and compute live in infrastructure you control, whether that’s a VPC or a server in a closet. “Managed” can be either — a cheap managed service is multi-tenant (your neighbor’s traffic shares the same control plane), while a serious one offers single-tenant isolation inside its own infrastructure. That distinction matters more than the self-vs-managed label itself, and it’s the first thing to pin down in any evaluation.
If you want the full breakdown of how this split plays out on a specific open-source stack, our n8n Self-Hosted vs Cloud for AI Agents comparison walks through the same tradeoff concretely.
How do security and data sovereignty actually differ — beyond the marketing?
Self-hosted gives you full data residency and audit control but makes you the security team; managed vendors carry certifications but hold your data on their rails. The real question is which security surface you’re actually better at defending.
Here’s the uncomfortable truth the marketing glosses over: self-hosting doesn’t make you more secure, it makes you more responsible. When you run your own stack, you own patching, secrets rotation, dependency vulnerabilities, and the incident response playbook. Your data may never leave your network — and for regulated industries, that’s genuinely non-negotiable — but your security posture is only as strong as the hours your team puts into defending it.
A serious managed platform inverts that equation. It carries the certifications — SOC 2, often ISO 27001 — and runs a hardened control plane with role-based permissions, audit trails, and managed secrets. Your data sits on their rails, which is the exact thing that makes architects nervous, but the honest framing is that a vendor whose entire business is security has more to lose from a breach than you do from a misconfigured firewall at 11pm.
What you should demand from either path is the same checklist: who can read your data, where does it physically reside, and can you see every action in an audit trail you control? “Managed” only means “opaque” if the platform won’t show you those three things. If it won’t, walk — that’s a toy wearing an enterprise costume.
What does each actually cost — and where are the hidden costs?
Self-hosted looks cheaper on the sticker but bills you in ops hours, uptime, patching, and idle GPU capacity; managed front-loads a subscription but folds in the substrate. The line item that flips the math is your own time.
Run the numbers honestly and the sticker price is a rounding error. A self-hosted setup might cost you a few hundred a month in compute, while a managed platform charges a per-employee subscription. But self-hosting doesn’t bill you in dollars — it bills you in you. Every upgrade, every security patch, every 3 a.m. alert, every hour of idle GPU you forgot to scale down is engineering time that isn’t going into the thing that actually differentiates your product.
That’s the concession worth making explicitly: your own engineering hours are the most expensive line item in the entire build, and the TCO math flips depending entirely on how many of those hours the platform returns to you. A solo architect with a depth advantage in cognition but no interest in being an on-call SRE will often find managed cheaper in real terms, even when the invoice is larger.
The inverse holds too: at high scale, or when you’re already running serious infrastructure, the per-seat managed premium can exceed what it’d cost you to self-host — if you’ve already amortized the ops team. There’s no universal answer, only a break-even point that moves with your team size and your tolerance for ops. Our AI Agent Platform Total Cost of Ownership guide does the full hidden-cost accounting so you can find where your own break-even sits.
Can you extend a managed platform — or do you hit a ceiling?
The ceiling is the real question, and it’s the one that separates a platform from a toy. A toy caps you at its UI; a serious platform exposes primitives — APIs, code hooks, custom tools, and the underlying model and logic.
Let’s be concrete about what “reaching the primitives” actually means, because this is where you should be ruthless in evaluation. A platform with real depth gives you:
- An API and SDK, not just a drag-and-drop canvas — so your build lives in version control, not in a UI state you can’t diff.
- Custom tool definitions — the ability to wrap any function, any internal API, any model call, and register it as a first-class tool.
- Webhooks and code hooks — so you can intercept and modify behavior at the points that matter, not just at the edges the vendor permits.
- Versioned, exportable logic — so your agent’s reasoning is a text artifact you can review, branch, and take with you.
The honest part is that even a good managed platform does draw a line somewhere — usually at the very bottom of the orchestration layer. You’re not going to rewrite the scheduler or the memory backend. The test isn’t “does it do everything raw code does”; it’s “does it expose everything I need above the substrate, and is the line it draws somewhere I don’t care about?”
Before you commit to any framework or platform, run that test deliberately. If framework-level depth is your benchmark, our comparisons of AutoGen vs CrewAI and Dify vs n8n show what “reaching the primitives” looks like across the open-source landscape.
How do you avoid lock-in — and what does a clean exit look like?
Lock-in is about data and logic, not just hosting. Prefer exportable definitions, versioned workflows, and open formats, and confirm you can take your prompts, tools, and memory with you.
This is the section where you find out whether a platform actually respects you. Lock-in rarely comes from the hosting itself — spinning up a new server is easy. It comes from the black-box state: the proprietary workflow format, the prompts locked inside a UI, the memory that only exists in someone else’s database.
Run this exit checklist against anything you’re evaluating, and treat a “no” on any of these as disqualifying:
- Can I export my workflow definitions in a readable, open format (JSON, YAML, code) rather than a vendor-only blob?
- Do I have API access to my own data — every prompt, every conversation, every stored memory?
- Is my logic versioned and portable, or does it only live as a UI state?
- Is there any proprietary black-box state — something the platform holds that I can’t reconstruct myself?
If the answer to all four is yes, “lock-in” reduces to a migration cost you can actually price. If any answer is no, you’re not buying a platform — you’re renting a dependency, and the exit will be priced at whatever the vendor decides it should be. An architect who takes exit this seriously is the one a serious platform actually wants as a customer.
Self-hosted vs managed: a decision framework for architects
The choice resolves to three questions — sovereignty needs, engineering bandwidth, and how much of the substrate you want to own. Everything else is justification after the fact.
Let’s make it decisive instead of hedged. Here’s the honest matrix:
| Axis | Self-Hosted | Managed |
|---|---|---|
| Security | Full residency and audit control; you are the security team | Certifications (SOC 2) and a hardened control plane; data on vendor rails |
| Cost | Low sticker, high ops-hours bill; idle capacity is yours to eat | Higher subscription, folds in substrate and uptime; predictable |
| Control | Total — every layer, every primitive, no ceiling | Primitives exposed above the substrate; a line drawn at orchestration |
| Exit | Yours by default — but only as clean as your own discipline | Clean only if exportable formats and API access are confirmed up front |
The decisive part is honest about when each wins. Self-host when you have regulated data that legally cannot leave your infrastructure, a hard cost ceiling that a per-seat premium would breach, or full-stack control as an actual product requirement — not a preference. Go managed when your team is small, shipping speed is the constraint, and the security and compliance burden is something you’d genuinely rather not own.
Now, the category this comparison cannot fully score, so I’ll say it plainly before it matters: full disclosure — we build one. EmployAIQ is a managed AI-workforce platform, and it sits in the “managed” seat of this exact table. The honest line between the two worlds is this: n8n is a toolkit you assemble; EmployAIQ is employees you hire. Neither is a better version of the other — they answer different questions. If what you want is to own the skill and the substrate end to end, self-hosting an open-source stack is the right answer for you, and no managed platform should try to talk you out of it.
But if what you actually want is to spend your depth on designing the cognition — the roles, the reasoning, the memory, the audit trail — rather than on rebuilding the plumbing beneath it, then a managed platform that ships primitives, permissions, memory, and an audit trail as standard is the door that matches. That’s the real resolution of the false choice this article started with: you don’t have to choose between a toy and reinventing the substrate. You can design production-grade AI employees from scratch without rebuilding the plumbing.
Where that line lands for you is the personal answer this framework exists to surface — and our no-code vs code decision framework, autonomous vs assisted architecture guide, and AI agents vs RPA breakdown each sharpen one edge of it.
Frequently asked questions
Is self-hosted always more secure than managed?
Not inherently. Self-hosted gives you control of residency and audit, but security is only as good as your own patching and ops. A managed platform with SOC 2 and a hardened control plane can be the safer default for most teams.
Does managed mean I lose control over the model?
No, on a serious platform. You still choose the model, prompts, tools, and logic. What you delegate is the substrate — hosting, orchestration, secrets, upgrades — not the cognition.
Can I move off a managed platform later?
Yes, if you design for exit: prefer exportable workflow definitions, versioned prompts, and API access to your own data. Confirm the vendor gives you your logic and memory in an open format before you commit.
Is “single-tenant” the same as self-hosted?
No. Self-hosted is almost always single-tenant, but managed platforms can offer single-tenant isolation inside their own infrastructure. The isolation matters more than the self-vs-managed label — confirm tenancy separately from deployment.
The bottom line
The false choice was never really between two platforms. It was between a toy that caps you and a full rebuild that buries your best hours in plumbing you didn’t want to own in the first place. Both are ways of being underestimated.
The way out is to treat the substrate as a commodity — owned by you or owned by a vendor, whichever makes the security, cost, and control math work — and spend your depth where it actually compounds: on the cognition, the reasoning, the memory, the audit trail. That’s the work only an architect can do, and it’s the part that can’t be handed to a tool.
Want to design AI employee roles from scratch rather than deploy templates? The AI Agent Architects runs as a small five-week cohort, and the waitlist hears every enrolment date first: Join the AI Agent Architects waitlist
About the Author
Anthony Odole is a former IBM Senior Managing Consultant, where he served as Enterprise Architect on Fortune 500 engagements, and the founder of AIToken Labs. He helps business owners cut through AI hype by focusing on practical systems that solve real operational problems.
His flagship platform, EmployAIQ, is an AI Workforce platform that enables businesses to design, train, and deploy AI Employees — AI agents that function as digital workforce members — that perform real work without adding headcount.